
Our current vulnerability management system can’t keep up
Frontier AI models can now find novel, chained zero-day vulnerabilities in open source software at machine speed.
The time between a vulnerability being discovered and being exploited has collapsed from years to hours. That means a growing share of exploits will be weaponized before the bug is ever publicly disclosed. Left alone, the default outcome is fragmentation. Every cloud, vendor, and security team will quietly fork the same critical dependencies with its own patch set. There will be no shared truth about what's actually fixed.
Fragmentation is slower, weaker, and more dangerous for everyone.
What Athena does
Athena is the industry coalition for the orchestrated defense of open source software. Members with access to any frontier AI model submit vulnerability findings to Athena. Operationally, they submit findings through an encrypted portal. We deduplicate and enrich each finding, tracing when the flaw was introduced, whether it's already fixed at HEAD, and publish the metadata as a private OSV feed.
Submitting members also get anonymized, aggregated intelligence across all coalition submissions. Affected projects are rebuilt as private, hardened versions, available to members through Chainguard Libraries before disclosure for 30 days. Findings are addressed in batches across a whole library, hardening it against entire classes of issues. This ensures scanners stay quiet even when a more capable model arrives.
Vulnerability and patch information is then passed to technology, platform, infrastructure, and cybersecurity partners that sit in front of much of the internet. These partners take this data and use it to push non-patch mitigations such as detection signatures, traffic-level rules, and platform-side blocks that stop exploits ahead of a vulnerability’s public disclosure. This acts as another layer of protection on top of providing the patch.
A patch only helps people who can apply it, and most of the world can’t move on an attacker’s timeline. The same dependencies that run inside the biggest banks also run a rural water plant or a regional hospital with one IT person and no security team. These organizations won’t patch in time, so we deliver these non-patch mitigations with no action required from the people they protect.
The coalition drives coordinated disclosure upstream. We are a premier partner of the Linux Foundation’s Akrites initiative, which is spinning up a Security Incident Response Team to ensure every fix is upstreamed to its project’s home on the maintainers' terms if the vulnerability exists in the latest version. When only older versions of the dependency are vulnerable, Chainguard drives disclosure and makes patch files available to everyone on disclosure day.
Together with this coalition of submitters across critical industries, technology platforms, cybersecurity partners, and global professional services, we are shielding the ecosystem and surfacing zero-day vulnerabilities at scale. So, whether you’re an Athena member or not, everyone stays protected from the incoming wave of AI threats.
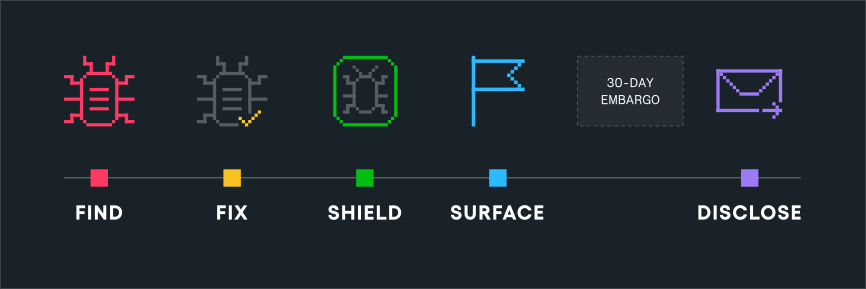
Find - The bug gets submitted through the encrypted portal, deduplicated, and enriched.
Fix - A hardened fix gets built under embargo, before any of it is public.
Shield - While the embargoed fix works its way toward upstream, cyber partners shield it at the network, traffic, and endpoint levels.
Surface - Chainguard publishes the OSV record; partners flag every customer still on a vulnerable version.
Disclose - The embargoed fix is handed to Akrites, disclosed upstream, and driven home for good.
Latest updates
- Athena's disclosures beginSep 28, 2026
- The flood is coming and the pipes were already fullSep 15, 2026
- This Shit is Hard: Patching a vulnerability that has no fixAug 17, 2026
- This Shit is Hard: How Chainguard is sandboxing AthenaJul 29, 2026
- Follow the moneyJul 15, 2026
- Summer of ClearinghousesJul 5, 2026
- Expanding AthenaJul 7, 2026
The coalition members


Every coalition member closes a gap others can’t
Submitters - Contribute vetted, pre-disclosure findings the whole system runs on.
Platforms - Stop exploits with network, endpoint, and traffic-level rules where a patch isn’t yet available or deployed.
Cybersecurity vendors - Add their own detections, signatures, and virtual patching as another layer of protection.
Global professional services - Help submitters deploy fixes at scale ahead of public disclosure.
What the coalition is saying

"Trust is at the core of what we do. Our clients count on BNY to protect what matters most, including the software behind our systems. As AI speeds up the discovery of vulnerabilities, Athena may help us identify and address risks earlier."
Dave Robinson
Chief Information Security Officer, BNY
Live today and building AI attack protection for all
More than two dozen organizations participating today, and disclosures have already begun.
21,175
Validated zero days
Athena powers zero-day protections for Chainguard customers
On disclosure day, patches for Athena members are made available to all Chainguard Libraries customers, stopping attack paths before bad actors can ever launch their campaign.
Join Athena
If any of this resonates, the next step is a single conversation. Reach out to us if you're finding vulnerabilities, want to join the coalition, or just curious to learn how your team can help. No one can get ahead of this alone, which is the whole point of a coalition. The more of the industry that participates, the less any attacker has left to find. Join us.